Core Capabilities
- • Shadow IT, Shadow AI & Asset Discovery — Discovers devices, unsanctioned applications and AI tools in use across the organization — including uploads to SaaS and AI services — so nothing operates outside your view.
- • Real-time Malware Detection — Behavioral analysis and signature-based scanning identify threats as they emerge, not after the damage is done.
- • Data Loss Prevention (DLP) — Monitor and block unauthorized exfiltration of sensitive data across endpoints, browsers, and email.
- • Browser Firewall & Anti-Phishing — Protect against phishing, malicious downloads, and credential harvesting at the endpoint level.
- • Insider-Threat Behavioral Analytics — Establish baselines for each endpoint and alert on deviations that may indicate insider threats or compromised accounts.
- • Geolocation Threat Mapping — Visualize the geographic origin of detected threats in real time on an interactive global map.
- • PowerShell & Python Agents — Lightweight collection agents for Windows (PowerShell) and Linux/macOS (Python) with minimal resource footprint.
Security Impact
Endpoints are often the first place where cyberattacks, data leaks, and compromised accounts become visible. Without continuous endpoint monitoring, suspicious activity can remain undetected until it affects critical systems, sensitive data, or business operations.
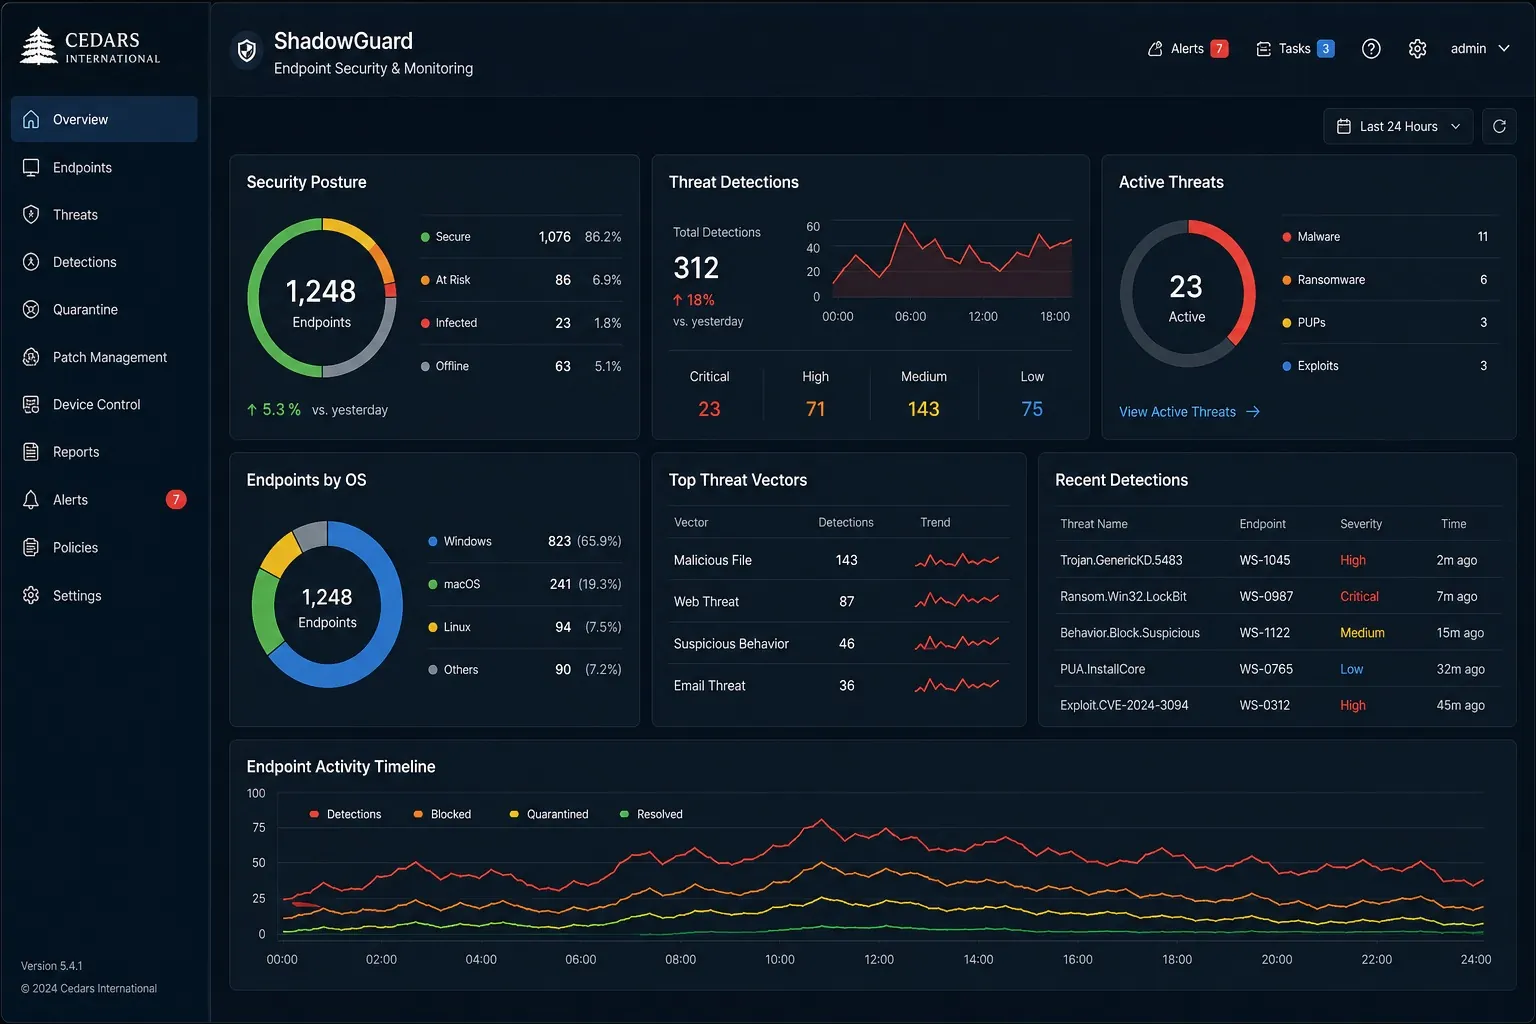
ShadowGuard gives security teams real-time visibility across their device environment, helping them identify threats earlier, respond faster, and reduce the risk of endpoint incidents spreading across the organization.
Business Outcomes
Detect Threats Earlier
Identify malware, suspicious processes, unusual user behavior, and potential account compromise before they develop into larger security incidents.
Protect Sensitive Data
Monitor and control how sensitive information is accessed, transferred, downloaded, or shared across endpoints, browsers, and email.
Reduce Investigation Time
Centralized endpoint telemetry and cross-module correlation give security teams the context needed to understand incidents and respond more efficiently.
Strengthen Security Across Every Device
Maintain continuous visibility and protection across Windows, Linux, and macOS devices from one centralized platform.
Improve Compliance and Accountability
Create a clearer record of endpoint activity, security events, policy violations, and response actions to support audits and compliance requirements.
Limit the Impact of Compromised Endpoints
Connect endpoint activity with threat intelligence, SIEM and other CCDS data to detect wider attack patterns and prevent isolated incidents from spreading.
How It Works
ShadowGuard agents run silently in the background, continuously collecting endpoint telemetry and forwarding it to the central CCDS analytics engine, where they are baselined against normal employee and machine behavior. Events are correlated with data from SIEM, Cedars Threat Intelligence and the other CCDS domains, so a suspicious process on one endpoint can automatically trigger enhanced monitoring and cross-domain threat classification platform-wide.
Ready to get started?
Contact us to get more information or schedule a quick demo