What It Does
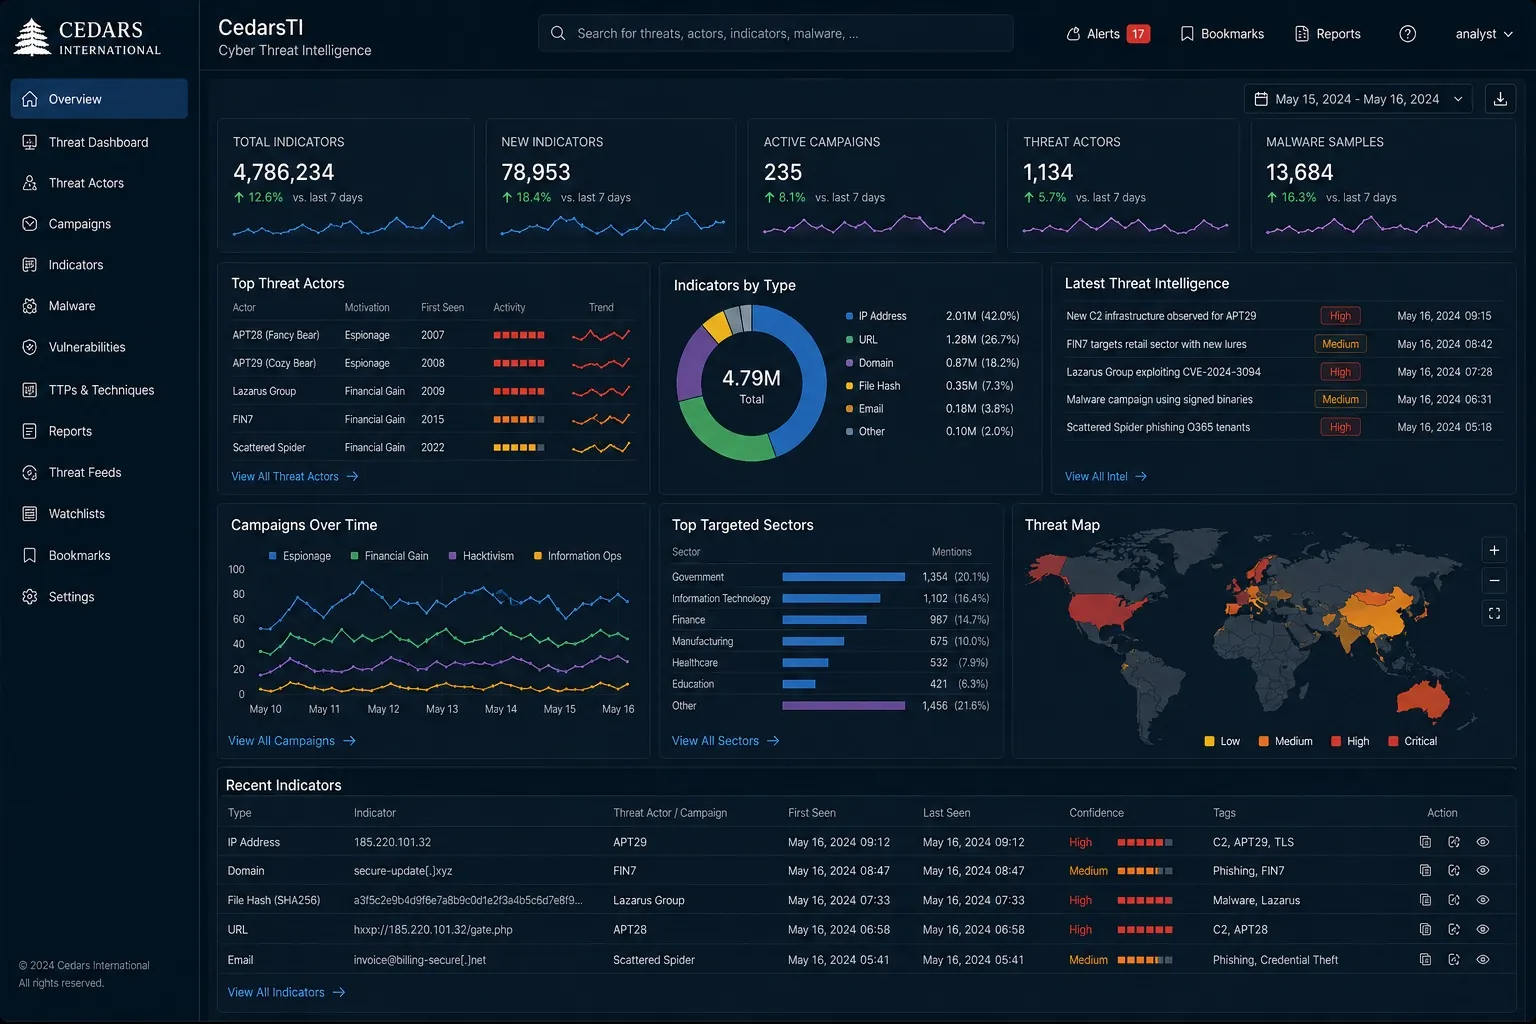
- • Website Monitoring — Continuously checks all your registered websites and web assets for availability, response time, and content integrity, alerting immediately when a site goes down, responds slowly, or shows signs of defacement.
- • Credential Leak Detection — Monitors dark web forums, paste sites, and breach databases for leaked credentials associated with your organization's domains, alerting your team before attackers can use them.
- • Threat Intelligence Feeds — Integrates with multiple threat intelligence sources and normalizes them into a unified feed, enriching each alert with threat actor, campaign, TTP, geographic origin, and historical activity.
- • IOC Management & Matching — Automatically checks all incoming logs and events from SIEM and ShadowGuard against Cedars Threat Intelligence's IOC database — malicious IPs, domains, file hashes, email addresses, and URLs — triggering immediate high-priority alerts.
- • APT Campaign Tracking — Tracks known Advanced Persistent Threat groups and their current campaigns, alerting your team when indicators matching known APT activity appear in your environment.
Security Impact
Many cyber threats become visible outside the organization before they reach internal systems. Leaked credentials, malicious infrastructure, active threat campaigns, and compromised public-facing assets can provide early warning of a potential attack.
Cedars Threat Intelligence gives security teams continuous visibility into these external risks, helping them identify relevant threats earlier, prioritize their response, and reduce the chance of external exposure becoming an internal security incident.
Business Outcomes
Identify External Threats Earlier
Detect exposed credentials, malicious infrastructure, and threat activity before they can be used against the organization.
Reduce Intelligence Noise
Combine and enrich intelligence from multiple sources so security teams can focus on threats relevant to their environment.
Accelerate Investigations
Provide analysts with context about indicators, threat actors, campaigns, and attack techniques to support faster decision-making.
Protect Public-Facing Assets
Monitor websites and external assets for outages, performance issues, unauthorized changes, and signs of compromise.
Strengthen Proactive Defense
Use current threat intelligence to improve threat hunting, monitoring, detection rules, and incident preparation.
Integration with CCDS
When Cedars Threat Intelligence detects a credential leak for a user, it immediately signals SIEM to increase authentication monitoring for that account, ShadowGuard to heighten endpoint alerting, Security Awareness to schedule urgent phishing training, and GRC to update the risk register — all automatically through the CCDS cross-domain correlation engine.
Ready to get started?
Contact us to get more information or schedule a quick demo